Episodes
91
Sept. 23, 2025
Leading Under Fire: Legal and Leadership Lessons from Cyber Crises
In this episode, Dr. Dave Chatterjee speaks with Josh Cook, a seasoned cybersecurity and privacy attorney who has guided multinational corporations and mid-sized businesses through high-stakes cyber crises. Drawing on his experience as the first Global Cyber Counsel for a Fortune Global 500 company, Cook shares how he built a global cyber legal function from scratch and why legal teams must be engaged long before an incident occurs. Together, they explore the human, organizational, and legal dynamics of crisis leadership: from building attorney-client privilege into preparation, to developing muscle memory through tabletop exercises, to ensuring the C-suite speaks with one unified voice when every second counts. Anchored in Dr. Chatterjee’s Commitment–Preparedness–Discipline (CPD) framework, the discussion underscores how legal, leadership, and security functions must converge to preserve trust and resilience in the face of relentless cyber threats.
90
Sept. 8, 2025
AI vs. AI: Automating Defense to Outpace Automated Attacks
In this episode, Dr. Dave Chatterjee speaks with Roi Cohen, CEO and Co-Founder of Vicarius, about the urgent need to counter AI-driven attacks with equally automated defenses. Cohen, who began his career managing mission-critical systems in the military, shares his journey through leadership roles at CyberArk and the launch of Vicarius. Drawing from real-world penetration tests at hospitals and Ivy League institutions, he illustrates how attackers exploit simple misconfigurations to access sensitive data. Together, they examine why defenders must move beyond manual, ticket-based remediation to keep pace with adversaries leveraging agentic AI. The conversation highlights that automation, while essential, is insufficient without human oversight and governance discipline. Anchored in Dr. Chatterjee’s Commitment–Preparedness–Discipline (CPD) framework, the discussion highlights the organizational mindsets and technological building blocks needed to sustain resilience. Cohen emphasizes …
89
Aug. 26, 2025
Beyond Passwords: Making Identity-Based Attacks Impossible in the Age of AI
In this episode, Dr. Dave Chatterjee sits down with Jasson Casey, CEO & Co-Founder @ Beyond Identity, to dissect the growing threat of identity-based attacks, which now account for nearly 80% of breaches. Casey explains how adversaries increasingly “log in” instead of breaking in, leveraging techniques such as MFA fatigue, session hijacking, and phishing kits. He shares lessons from his professional journey—ranging from building telco networks to advising the U.S. Government and launching Beyond...
88
July 21, 2025
Closing the Remediation Gap with Agentic AI
In this compelling episode, Dr. Dave Chatterjee engages with John Amaral, a serial entrepreneur and cybersecurity innovator, to explore how his company Root is using agentic AI to tackle one of cybersecurity’s biggest challenges—remediation delay. The conversation unpacks the dangers of security debt, the power of human-AI collaboration in patching vulnerabilities, and how organizations can evolve from reactive to proactive postures. The discussion also explores the limitations of AI, the critic...
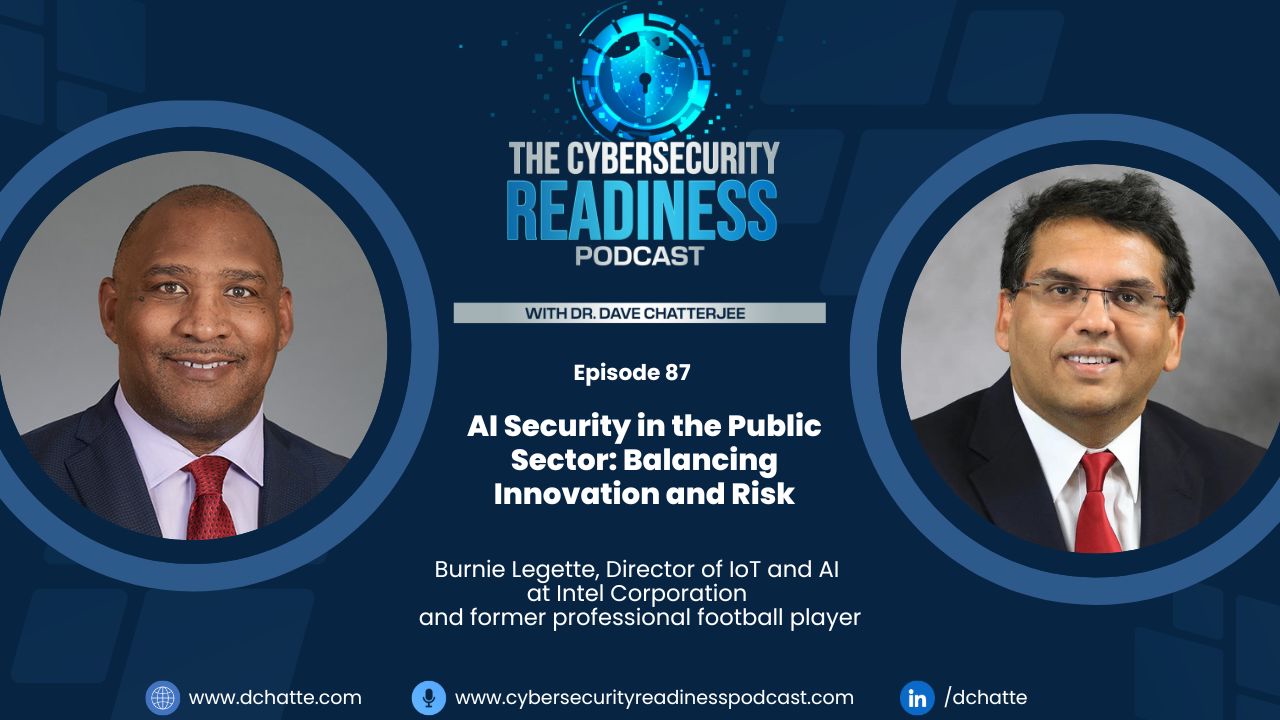
87
June 17, 2025
AI Security in the Public Sector: Balancing Innovation and Risk
In this episode, Dr. Dave Chatterjee is joined by Burnie Legette, Director of IoT and AI at Intel Corporation and former professional football player. Their conversation explores the evolving landscape of AI deployment within the public sector, with a particular focus on the security challenges and governance strategies required to harness AI responsibly. Drawing on his cross-sectoral experience, Burnie offers insights into the cultural, technical, and ethical nuances of AI adoption. Dr. Chatter...

86
May 17, 2025
Holistic Identity Security: Shifting the Paradigm from Reactive to Proactive
In this compelling episode, Dr. Dave Chatterjee is joined by Damon Fleury, Chief Product Officer, SpyCloud to dissect one of cybersecurity’s most exploited and least understood attack surfaces—identity. With nearly three decades of experience in security, Damon shares real-world insights into how identity compromises serve as the entry point for major breaches, why a holistic approach to identity security is urgent, and how organizations can move from reactive defense to proactive resilience. Th...

85
May 3, 2025
From Botnets to AI: Defending Against the Future of DDoS Warfare
In this episode of the Cybersecurity Readiness Podcast, Dr. Dave Chatterjee sits down with Richard Hummel, Director of Threat Intelligence at NETSCOUT, to unpack the fast-evolving Distributed Denial of Service (DDoS) threat landscape. Richard shares unique insights from NETSCOUT’s latest global threat intelligence report, discussing the strategic weaponization of DDoS attacks in geopolitical conflict, the role of AI in modern attack infrastructure, and why proactive preparation, not prevention, ...

84
April 22, 2025
Stopping Social Engineered Vishing Attacks Before They Start
Social engineering continues to be the primary gateway for cyberattacks, responsible for nearly 80% of fraud and ransomware incidents. And notably, 1 in 4 of these social engineering attacks originate via phone calls. Yet many enterprises continue to leave their phone systems exposed. In this episode, Dr. Dave Chatterjee engages Richard Quattrocchi, Vice President of Digital Transformation, Mutare Inc., in a compelling discussion on the often-overlooked threat of voice-based cyberattacks, partic...

83
March 31, 2025
Future-Proofing Your Data: Preparing for the Post-Quantum Era
Dr. Dave Chatterjee and David Close discuss the implications of post-quantum cryptography (PQC) on cybersecurity readiness. David, a Chief Solutions Architect at Futurex, explains the evolution of cryptographic methods to counter quantum computing threats. He highlights the importance of NIST's role in standardizing quantum-resistant algorithms like Kyber and Dilithium. David shares practical examples, such as Google and Cloudflare's hybrid TLS implementation and a financial institution's use of...

82
March 4, 2025
Securing AI's Blind Spots: The Hidden Risks in Enterprise AI Adoption
The adoption of Artificial Intelligence (AI) and Generative Artificial Intelligence (Gen-AI) applications and tools are exploding. The global AI infrastructure market is projected to reach over $96 billion by 2027. AI applications are being used to empower every organizational function and industry, from logistics and supply chain to manufacturing, healthcare, finance and banking, marketing and sales, and customer sales. However, such adoption and use of AI tools and platforms has greatly expand...

81
Feb. 17, 2025
Elevating Your Offensive Security Program
Dr. Dave Chatterjee hosts a discussion on elevating your offensive program with Mark Carney, CEO @ Evolve Security, and Yaron Levi, Chief Information Security Officer (CISO) at Dolby Labs. They emphasize the importance of a proactive, continuous approach to cybersecurity, contrasting it with traditional reactive measures. Key points include the need for a threat-informed, programmatic mindset, continuous threat exposure management (CTEM), and the integration of business objectives. They stress t...

80
Feb. 2, 2025
Using Blockchain Technology to Make Messaging Apps More Secure and Private
Dr. Dave Chatterjee and Kee Jefferys, Technical Co-Founder of Session, discuss the use of blockchain technology in enhancing the security and privacy of messaging apps, specifically Session. Session, which has over a million monthly active users, uses a decentralized network of nodes incentivized by Session tokens. Unlike traditional messaging apps, Session does not require a phone number for sign-up and employs onion routing and end-to-end encryption to protect user data. Kee emphasizes the imp...
79
Jan. 12, 2025
Authenticate without Storing Credentials: MIT Scientist Cracks the Code
Despite companies’ best efforts, stored access credentials inevitably get stolen or misused. Whether it is a disgruntled employee posting the data, an employee that makes an innocent mistake exposing that data, a company needing revenue selling the information, a criminal hacker group stealing the information, or a government-backed group stealing the information, etc. it is simply a matter of when not if that information will be stolen. “The only truly safe way to handle people’s secrets is ne...

78
Dec. 30, 2024
Lessons from 2024's Biggest Cyber Incidents and Building Stronger Defenses for 2025
In this episode, Shrav Mehta, Founder, and CEO at Secureframe, joins me to discuss major cybersecurity incidents in 2024, highlighting five significant breaches: National Public Data (2.7 billion records), AT&T (50 billion), Ticketmaster (500 million), Change Healthcare (145 million), and Dell (49 million). We emphasize the importance of proactive measures, such as data minimization, continuous training, and zero-trust models. I stressed the need for leadership engagement, robust incident respon...

77
Dec. 13, 2024
Stopping Deepfake Threats Through Identity Verification
In this episode, Aaron Painter, CEO at Nametag, joins me in discussing the Deepfake fraud phenomenon and how organizations and individuals should protect themselves from such scams. A recent study conducted by finance software provider Medius finds that over 53% of businesses in the U.S. and U.K. have been targets of financial scams powered by “deepfake” technology, with 43% falling victim to such attacks. 85% of the finance professionals polled view such scams as an “existential” threat to thei...

76
Nov. 19, 2024
From reactive to proactive: How behavioral psychology is transforming enterprise security
IBM recently reported a 71% year-over-year increase in attacks using valid credentials. This continued use of stolen credentials is also evident through ongoing public incidents like the string of attacks targeting Snowflake's customers that resulted in breaches at AT&T and Advanced Auto Parts. Lynsey Wolf, Team Lead and Insider Threat Analyst at DTEX Systems believes that users' psychological and behavioral traits are being overlooked when it comes to defending against credential misuse. In thi...

75
Nov. 1, 2024
Compliance in the Cloud: Challenges and Best Practices
Accelerating into the cloud without caution often brings complexities that can cause more harm than good. Gartner has noted that cloud configuration errors cause 95% of cybersecurity breaches. With the rapid pace of cloud adoption, less time is spent ensuring systems are built and operated effectively with proper cyber hygiene. In this episode, Dale Hoak, Director of Information Security at RegScale, joins me in discussing cloud compliance-related challenges and best practices. Here are some ter...

74
Oct. 20, 2024
Reducing the Risk of Social Engineering to Exploit IT Help Desk
In this episode, Mike Manrod, the Chief Information Security Officer (CISO) of Grand Canyon Education, and Ori Eisen, the Founder and CEO of Trusona, joined me to discuss how best to reduce the risks of social engineering attacks on IT support and help desk personnel. This episode was motivated by the major cyber attack that brought MGM Resorts International's operations to a screeching halt. It was a social engineering attack where the attackers gained super administrator privileges by providin...

73
Oct. 6, 2024
Unlocking Cyber Potential: The Power of Collaboration in K-12 Cyber Education
In this episode, Laurie Salvail, Ph.D., Executive Director of CYBER.ORG, joins me to discuss the importance of cybersecurity education for K-12 students. Primarily funded by the Cybersecurity and Infrastructure Security Agency (CISA), CYBER.ORG is a powerful and free resource available to K-12 students and educators in the United States. CYBER.ORG’s Range, a cloud-based virtual environment, empowers K-12 students with real-world cybersecurity skills in a secure platform. To access and download ...

72
Sept. 23, 2024
Large Language Model (LLM) Risks and Mitigation Strategies
As machine learning algorithms continue to evolve, Large Language Models (LLMs) like GPT-4 are gaining popularity. While these models hold great promise in revolutionizing various functions and industries—ranging from content generation and customer service to research and development—they also come with their own set of risks and ethical concerns. In this episode, Rohan Sathe, Co-founder & CTO/Head of R&D at Nightfall.ai, and I review the LLM-related risks and how best to mitigate them. To acc...

71
Sept. 2, 2024
Identity Continuity in Multi-Cloud Environments
The importance of maintaining uninterrupted services cannot be overemphasized, especially in light of the recent global IT outage fiasco. With the increasing dependence on cloud-based services, uninterrupted connectivity is essential to maintaining business continuity. Since identity providers control access to an organization's application and data, any downtime can shut down mission-critical operations. It was great to have Eric Olden, Co-Founder, Chairman, and Chief Executive Officer of Strat...

70
Aug. 20, 2024
Securing SMBs Serving Defense Industrial Base and U.S. Critical Infrastructure
In this episode, Chris Petersen, Co-Founder and CEO of RADICL, and I discuss the challenges of securing the small and medium-sized businesses (SMBs) that serve the United States defense industrial base (DIB) and critical infrastructure. These SMBs play a significant role in supporting the Advanced Defense Systems that protect our nation from domestic and international threats. So, it is imperative to review what it takes to keep these SMBs safe from cyber-attacks. To access and download the ent...

69
July 31, 2024
2024 Cyber Trends and Predictions: Global IT Outage and More
In this episode, John Funge, Managing Director at DataTribe, and I discuss the Global IT Outage caused by a flawed update to CrowdStrike's cloud-based security software. We also review DataTribe's recently published report on cybersecurity trends and predictions for 2024. In closing, John shares some tips and recommendations for those seeking cybersecurity funding. To access and download the entire podcast summary with discussion highlights -- https://www.dchatte.com/episode-69-2024-cyber-tren...

68
June 25, 2024
Fortifying Healthcare Data: Proactive Defense Strategies
The recent breach of the Change Healthcare platform serves as a strong reminder that the healthcare sector remains extremely vulnerable to different types of attacks. In late February, a ransomware gang known as Black Cat claimed responsibility for hacking Change Healthcare, a subsidiary of UnitedHealth Group. The intruders disrupted operations and stole up to four terabytes of data, including personal information, payment details, insurance records, and other sensitive information. It is also r...